About ComodoCA
Comodo CA is a subsidiary of Sectigo (formerly Comodo CA), a worldwide leader in digital web security solutions. Trusted by global enterprises for more than two decades, Sectigo provides digital identity solutions for businesses of all sizes, protecting their employees, customers, intellectual property, and overall brands from online threats. As the largest commercial certificate authority with over 100 million SSL certificates worldwide, Sectigo has the experience and know-how to help companies secure digital transactions and grow online trust.
Crl.comodoca.com Trojan Removal
This article can help you to remove Crl.comodoca.com Virus. The step by step removal works for every version of Microsoft Windows.
The appearance of the Crl.comodoca.com website is a clue. It is a warning sign that indicates an infection. Your device harbors a dangerous Trojan horse. Heed that warning. You are in a bad situation. The Trojan horses are considered the worst type of infection you can catch. Crl.comodoca.com is not an exception. This Trojan wastes no time. Once on board, it spreads around your entire system. In no time, you began to notice its influence. The Trojan causes program failures. Your anti-virus app gets disabled. Odd alerts pop up for no apparent reason. Your device becomes slow and unresponsive. Even your Internet connection seems slower than before. You often find yourself forced to reboot your system repeatedly. Yet, a simple restart won’t fix your problem. The Trojan loads together with your OS and is always running in the background. This invader messes with your system. It alters your settings and modifies your registry. It eats up space and resources. The parasite prevents you from using your computer normally. Yet, all these issues are nothing compared to the things that happen behind your back. Crl.comodoca.com Trojan opens a backdoor to your system. Adware, hijackers, worms, and even ransomware can use the Trojan to infect your computer. Do not risk it! Your best course of action is the immediate removal of the Trojan. The sooner you clean your computer, the better!
How did I get infected with?
The hackers don’t target individual victims. They use deception to spread their parasites. Crl.comodoca.com Trojan, too, uses trickery to invade. The virus hides in software bundles, torrents, and spam emails. It also lurks behind fake updates and rogue applications. All these methods rely on your carelessness and naivety. Your caution, on the other hand, can prevent them from succeeding. Even a little extra attention goes a long way. Avoid using torrents. Download your software from reputable sources only. Pay close attention to all installation processes. Forget about the “Next-Next-Finish” installation strategy. When available, select the advanced setup option. Also, read the terms and conditions. If you cannot spare enough time to read the whole document, you can use an online EULA analyzer to scan it. And, of course, be very careful with your inbox. The good old spam emails are still the number one Trojan distribution method. The crooks write on behalf of well-known organizations and companies. They attach corrupted files and well as malicious links, and prey on your naivety. You can download a virus with just one click. So, don’t click! If you receive an unexpected message, don’t interact with it. Take your time to verify the sender. You can enter the questionable email address into a search engine. You can also visit the sender’s official website. Let’s say your bank send you an offer via email. The first thing you should do is to go to their official website. Compare the email addresses listed there with the one you’ve received a message from. If they don’t match, delete the pretender immediately. Crl.comodoca.com Trojan tricked you once. Do not let other parasites deceive you ever again! Always do your due diligence!
Why is this dangerous?
The thing about Trojan horses is that they rarely come alone. Crl.comodoca.com virus, too, brings a whole array of parasites. The Trojan installs adware and hijackers. It is also quite capable of installing spyware. The nasty parasite takes aim at your privacy. It follows instructions to steal sensitive information. The crooks are usually after your personal and financial details. Crl.comodoca.com Trojan has no place on your computer. It wreaks your system and jeopardizes your privacy. This meddlesome parasite should be dealt with immediately. The more time you grant it on board, the worse your situation becomes. You cannot see it, but it always runs in the background. It’s just a matter of time before it discovers sensitive information. What’s worse, it may receive instructions to infect your computer with a devastating virus. Do not play with your luck. You cannot win against Crl.comodoca.com Trojan. The best thing you can do is to clean your computer.
Manual Crl.comodoca.com Removal Instructions
Please, have in mind that SpyHunter offers a free 7-day Trial version with full functionality. Credit card is required, no charge upfront.
The Crl.comodoca.com infection is specifically designed to make money to its creators one way or another. The specialists from various antivirus companies like Bitdefender, Kaspersky, Norton, Avast, ESET, etc. advise that there is no harmless virus.
If you perform exactly the steps below you should be able to remove the Crl.comodoca.com infection. Please, follow the procedures in the exact order. Please, consider to print this guide or have another computer at your disposal. You will NOT need any USB sticks or CDs.
STEP 1: Track down Crl.comodoca.com related processes in the computer memory
- Open your Task Manager by pressing CTRL+SHIFT+ESC keys simultaneously
- Carefully review all processes and stop the suspicious ones.
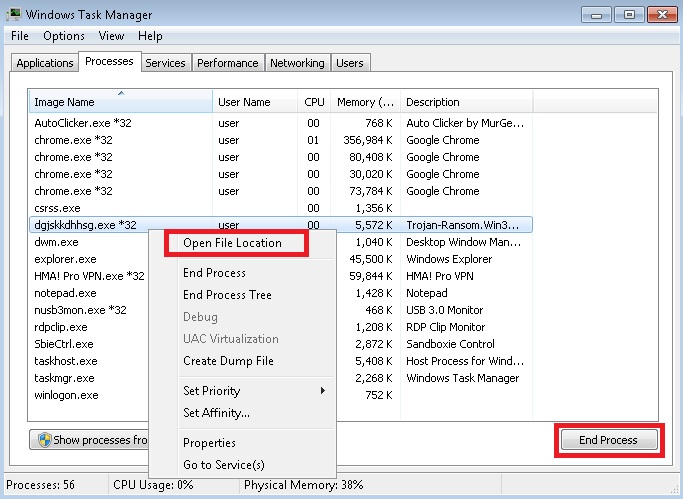
- Write down the file location for later reference.
Step 2: Locate Crl.comodoca.com startup location
Reveal Hidden Files
- Open any folder
- Click on “Organize” button
- Choose “Folder and Search Options”
- Select the “View” tab
- Select “Show hidden files and folders” option
- Uncheck “Hide protected operating system files”
- Click “Apply” and “OK” button
Clean Crl.comodoca.com virus from the windows registry
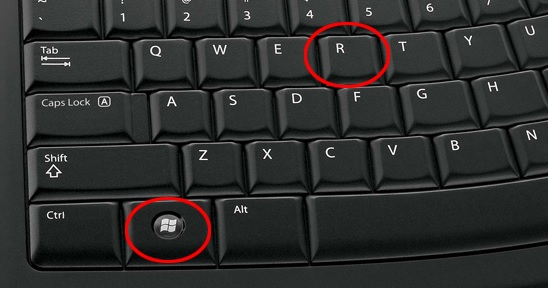
- Once the operating system loads press simultaneously the Windows Logo Button and the R key.
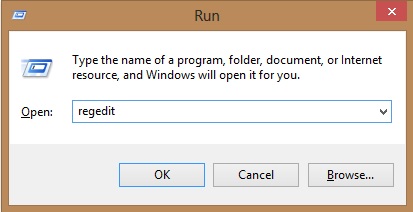
- A dialog box should open. Type “Regedit”
- WARNING! be very careful when editing the Microsoft Windows Registry as this may render the system broken.
Depending on your OS (x86 or x64) navigate to:
[HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run] or
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] or
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run]
- and delete the display Name: [RANDOM]
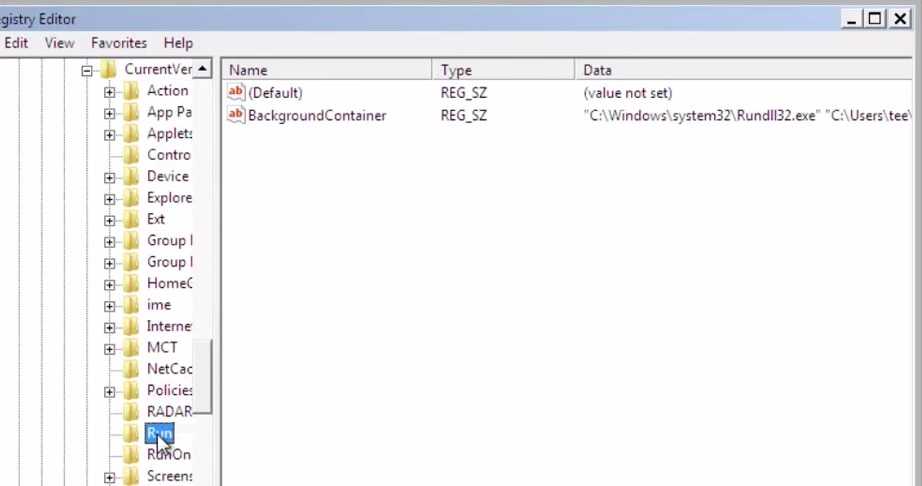
- Then open your explorer and navigate to: %appdata% folder and delete the malicious executable.
Clean your HOSTS file to avoid unwanted browser redirection
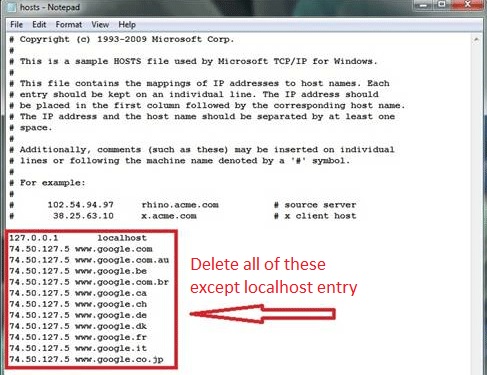
Navigate to %windir%/system32/Drivers/etc/host
If you are hacked, there will be foreign IPs addresses connected to you at the bottom. Take a look below:
Step 4: Undo the possible damage done by Crl.comodoca.com
This particular Virus may alter your DNS settings.
Attention! this can break your internet connection. Before you change your DNS settings to use Google Public DNS for Crl.comodoca.com, be sure to write down the current server addresses on a piece of paper.
To fix the damage done by the virus you need to do the following.
- Click the Windows Start button to open the Start Menu, type control panel in the search box and select Control Panel in the results displayed above.
- go to Network and Internet
- then Network and Sharing Center
- then Change Adapter Settings
- Right-click on your active internet connection and click properties. Under the Networking tab, find Internet Protocol Version 4 (TCP/IPv4). Left click on it and then click on properties. Both options should be automatic! By default it should be set to “Obtain an IP address automatically” and the second one to “Obtain DNS server address automatically!” If they are not just change them, however if you are part of a domain network you should contact your Domain Administrator to set these settings, otherwise the internet connection will break.
- Check your scheduled tasks to make sure the virus will not download itself again.
How to Permanently Remove Crl.comodoca.com Virus (automatic) Removal Guide
Please, have in mind that once you are infected with a single virus, it compromises your whole system or network and let all doors wide open for many other infections. To make sure manual removal is successful, we recommend to use a free scanner of any professional antimalware program to identify possible virus leftovers or temporary files.
Remove Ocsp.comodoca.com Pop-up Ads
Can’t Remove Ocsp.comodoca.com ads ? This page includes detailed ads by Ocsp.comodoca.com Removal instructions!
Do you get redirected to ocsp.comodoca.com and other bizarre websites? Are you unable to find what you search for online? Do you come across pop-up ads on a daily basis? Is your computer sluggish? You’re dealing with a parasite. The silver lining here is that this program is relatively easy to tackle. What you’re stuck with is a potentially unwanted adware infection. Those are more annoying than they are dangerous. However, don’t underestimate the intruder. The more time it spends on board, the more problematic it becomes. Are you willing to risk it? Your situation could become a lot worse if you hesitate for too long. Take action on the spot. You won’t regret it. On the other hand, you will regret keeping the virus on board. No cyber infection belongs on your machine. After all, malware gets developed to serve hackers’ malicious purposes. The adware starts messing with you immediately after installation. It adds an extension to your browsers. Thanks to this pesky plugin, the parasite takes control over your overall online experience. You’re about to witness numerous changes in your default browsing settings. It goes without saying all of them are completely unauthorized. Crooks don’t need to take your opinions into consideration. They inject your browsers with pop-ups for one very simple reason. The ocsp.comodoca.com pop-up ads are sponsored. By displaying them, crooks gain profit. Easy, illegitimate revenue is every single crook’s dream. That explains why the commercials are impossible to get rid of. Furthermore, a sponsored ad is never a reliable one. There are some corrupted ads on your PC screen so watch out for malware. If you click the wrong pop-up, you’ll automatically download more infections. Yes’ it’s that simple. Adware can’t cause you harm directly. It lets you do the job instead. To protect your PC, avoid the pesky ocsp.comodoca.com pop-up ads. These stubborn web links cover all websites you visit. Or, should we say, attempt to visit. Surfing the Web with an adware-type virus on board is, to say the least, difficult. Pop-ups, pop-unders, banners, interstitials, video ads, etc. In this mess of commercials, you must do the right thing. Restrain yourself from clicking the ads and delete the virus instead. This infection also puts in danger your private information. It collects browsing-related data such as passwords, usernames, browsing history. The parasite might get to some personally identifiable information as well. To prevent financial scams and identity theft, tackle the virus now.
How did I get infected with?
The easiest explanation is a freeware or shareware bundle. Many people use those to download a bunch of programs at once. However, many hackers use them too. Stay away from illegitimate program packages and websites. Check out what you’re about to download as well. Unless you make a thorough check, you might compromise your PC yourself. Never overlook a potential threat online. It is easier to prevent installation than to remove a virus after that. Save yourself the trouble. Take your time in the process. Skipping steps may leave your device open to parasites. In addition, go through the EULA or Terms and Conditions. You must be aware what you give green light to, right? Another tactic involves spam email-attachments. If you stumble across some random email from an unknown sender, delete it. Chances are, it’s immensely dangerous. The same piece of advice goes for your messages in social media. Be cautious and always make sure you outwit hackers.
Why is this dangerous?
The ocsp.comodoca.com pop-up ads are, without a doubt, malicious. These obnoxious links will lead you to unsafe websites. Before you know it, they might bring along further damage. As we mentioned already, the adware adds a plugin to your browsers. It’s compatible with Google Chrome, Mozilla Firefox and Internet Explorer. You don’t have a single reliable browser right now. Therefore, you’re forced to deal with the pop-ups all the time. This infection also redirects you to unknown pages that might turn out to be harmful. It causes your browsers to frequently crash. Even your Internet connection might become unstable all of a sudden. Last but not least, your privacy is now jeopardized. To delete the virus manually (which is a must), please follow our detailed removal guide. You’ll find it down below.
How to Remove Ocsp.comodoca.com virus
Please, have in mind that SpyHunter offers a free 7-day Trial version with full functionality. Credit card is required, no charge upfront.
The Ocsp.comodoca.com infection is specifically designed to make money to its creators one way or another. The specialists from various antivirus companies like Bitdefender, Kaspersky, Norton, Avast, ESET, etc. advise that there is no harmless virus.
If you perform exactly the steps below you should be able to remove the Ocsp.comodoca.com infection. Please, follow the procedures in the exact order. Please, consider to print this guide or have another computer at your disposal. You will NOT need any USB sticks or CDs.
Please, keep in mind that SpyHunter’s scanner tool is free. To remove the Ocsp.comodoca.com infection, you need to purchase its full version.
STEP 1: Track down Ocsp.comodoca.com in the computer memory
- Open your Task Manager by pressing CTRL+SHIFT+ESC keys simultaneously
- Carefully review all processes and stop the suspicious ones.
- Write down the file location for later reference.
Step 2: Locate Ocsp.comodoca.com startup location
Reveal Hidden Files
- Open any folder
- Click on “Organize” button
- Choose “Folder and Search Options”
- Select the “View” tab
- Select “Show hidden files and folders” option
- Uncheck “Hide protected operating system files”
- Click “Apply” and “OK” button
Clean Ocsp.comodoca.com virus from the windows registry
- Once the operating system loads press simultaneously the Windows Logo Button and the R key.
- A dialog box should open. Type “Regedit”
- WARNING! be very careful when editing the Microsoft Windows Registry as this may render the system broken.
Depending on your OS (x86 or x64) navigate to:
[HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run] or
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] or
[HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run]
- and delete the display Name: [RANDOM]
- Then open your explorer and navigate to: %appdata% folder and delete the malicious executable.
Clean your HOSTS file to avoid unwanted browser redirection
Navigate to %windir%/system32/Drivers/etc/host
If you are hacked, there will be foreign IPs addresses connected to you at the bottom. Take a look below:
STEP 3 : Clean Ocsp.comodoca.com traces from Chrome, Firefox and Internet Explorer
Open Google Chrome
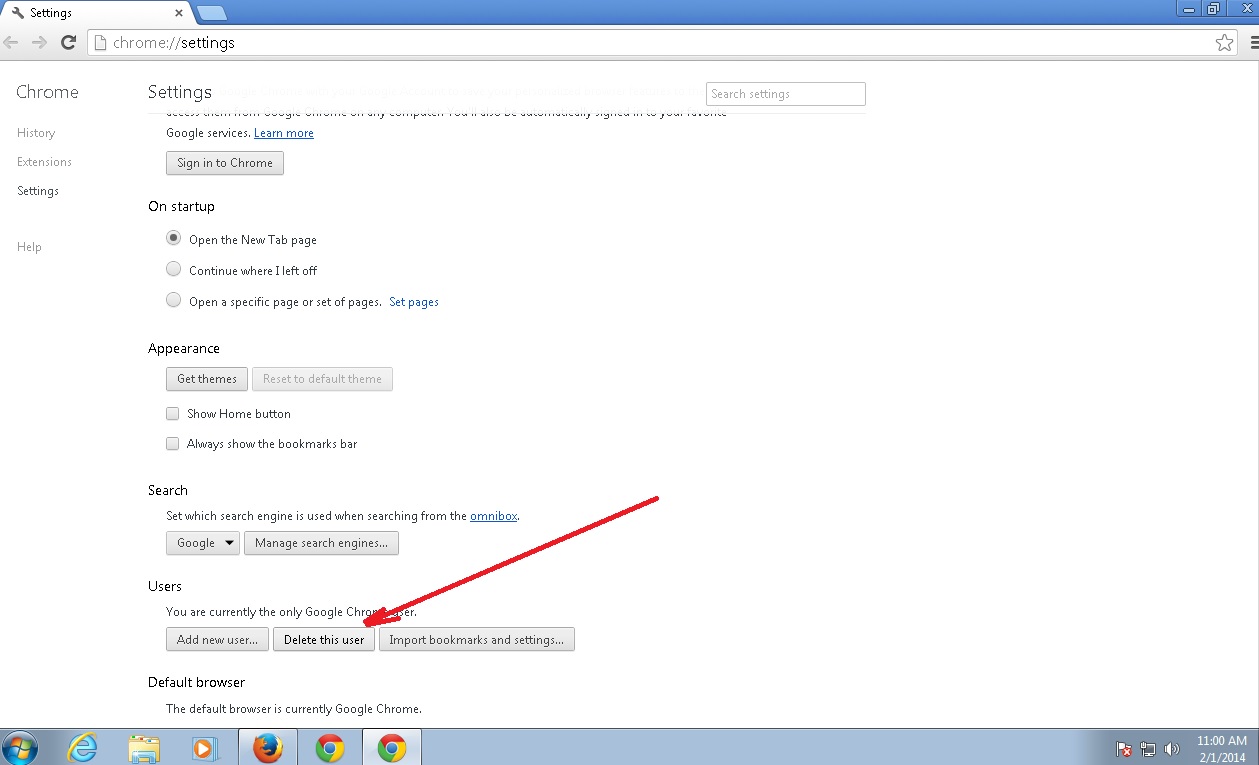
Open Mozilla Firefox
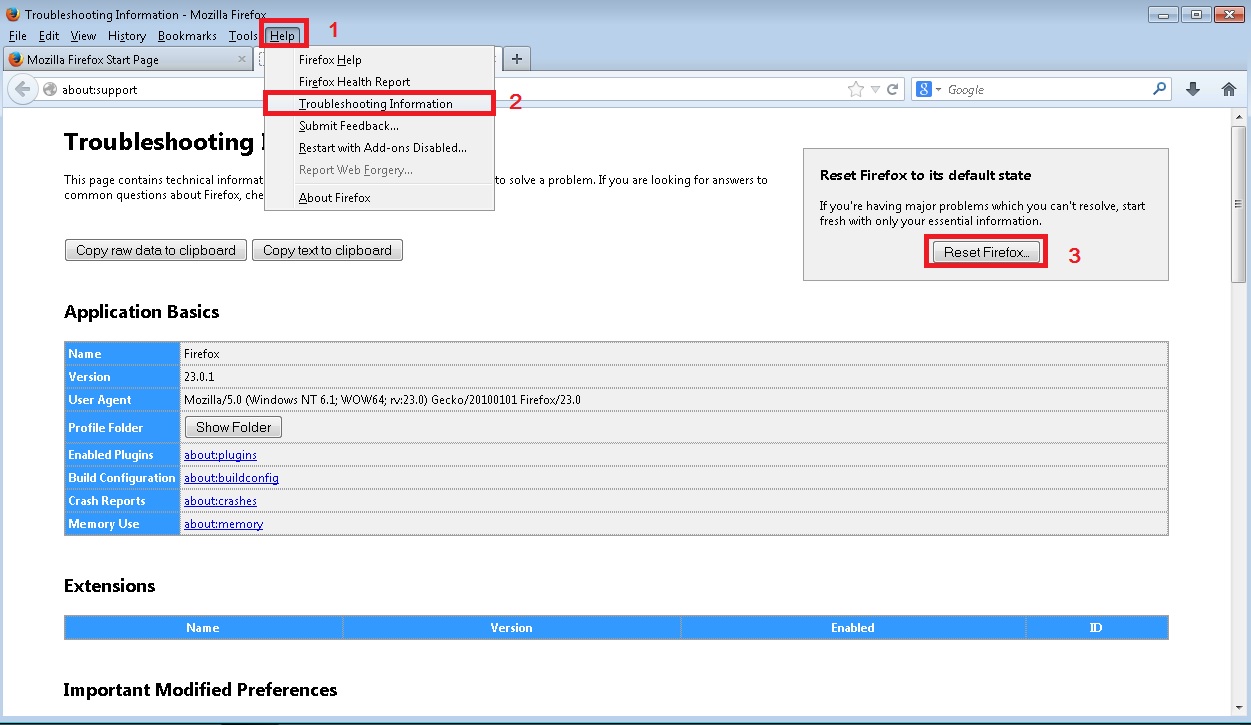
Open Internet Explorer
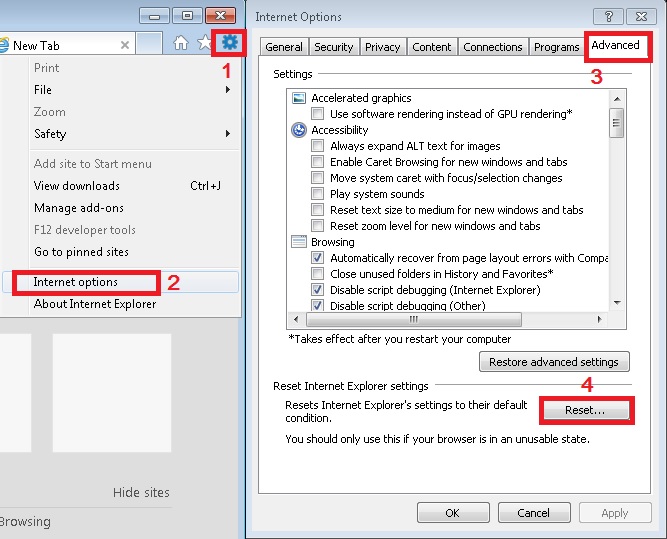
Step 4: Undo the damage done by Ocsp.comodoca.com
This particular Virus may alter your DNS settings.
Attention! this can break your internet connection. Before you change your DNS settings to use Google Public DNS for Ocsp.comodoca.com, be sure to write down the current server addresses on a piece of paper.
To fix the damage done by the virus you need to do the following.
- Click the Windows Start button to open the Start Menu, type control panel in the search box and select Control Panel in the results displayed above.
- go to Network and Internet
- then Network and Sharing Center
- then Change Adapter Settings
- Right-click on your active internet connection and click properties. Under the Networking tab, find Internet Protocol Version 4 (TCP/IPv4). Left click on it and then click on properties. Both options should be automatic! By default it should be set to “Obtain an IP address automatically” and the second one to “Obtain DNS server address automatically!” If they are not just change them, however if you are part of a domain network you should contact your Domain Administrator to set these settings, otherwise the internet connection will break.
You must clean all your browser shortcuts as well. To do that you need to
- Right click on the shortcut of your favorite browser and then select properties.
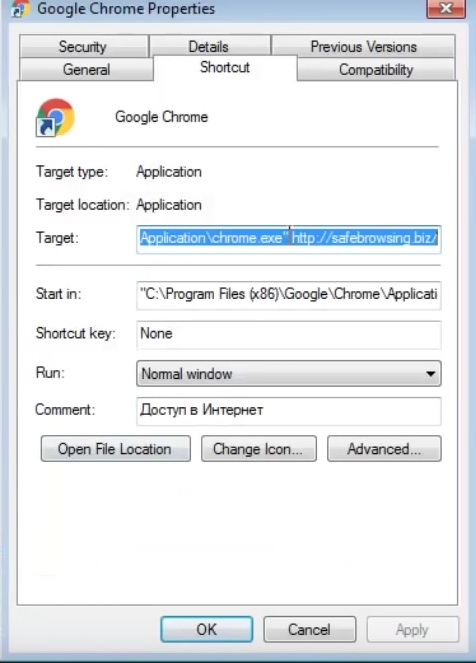
- in the target field remove Ocsp.comodoca.com argument and then apply the changes.
- Repeat that with the shortcuts of your other browsers.
- Check your scheduled tasks to make sure the virus will not download itself again.
How to Permanently Remove Ocsp.comodoca.com Virus (automatic) Removal Guide
Please, have in mind that once you are infected with a single virus, it compromises your system and let all doors wide open for many other infections. To make sure manual removal is successful, we recommend to use a free scanner of any professional antimalware program to identify possible registry leftovers or temporary files.
Ocsp comodoca com что это
SiteLock Website Protection
Automatically protect your website, reputation, and visitors against cyberthreats including malware, DDoS attacks, phishing scams, bad bots and other types of malicious code and cyber threats. This includes the protection of your site code and web applications.
of Fortune 1000
companies use Sectigo
market leader
in SSL certificates
businesses on the
Sectigo platform
SiteLock Basic
Basic scanning and backup
$14.99 €13.73 £11.83 AED 55.01 A$22.42 R$73.74 CA$20.04 CHF 12.79 DKK 102.37 IDR 232,892.11 ₹1,246.44 ¥2,177 MX$255.39 NZ$24.11 PHP 833.21 PLN 59.80 SAR 56.21 SEK 154.21 SGD 19.95 TRY 447.31
Complete onboarding & setup with 24/7 Access to Customer Support
- 30-hour ticket response time
Unlimited Automatic Malware Removal
- SiteLock Expert Team Removal Not Available
Website Backup (up to 2GB)
- Daily backups of website files and database
Daily Site Scanning, including:
- SSL scan
- Malware scan
- Spam scan
- SQL injection scan
- Cross-site scripting scans
- SiteLock Risk Score
Daily Code & Database Scanning, including:
- Codebase, database, and CMS scanning
- Vulnerability detection
SiteLock Pro
An added layer of website protection
$24.99 €22.88 £19.73 AED 91.71 A$37.38 R$122.93 CA$33.41 CHF 21.33 DKK 170.67 IDR 388,257.10 ₹2,077.96 ¥3,628 MX$425.77 NZ$40.19 PHP 1,389.06 PLN 99.69 SAR 93.71 SEK 257.09 SGD 33.26 TRY 745.71
Complete onboarding & setup with 24/7 Access to Customer Support
- 24-hour ticket response time
Unlimited Automatic Malware Removal
- Unlimited SiteLock Expert Team Removal (excludes pre-existing infections. For removal of pre-existing infections, SiteLock 911 is required)
Website Backup (up to 5GB)
- Daily backups of website files and database
Daily Site Scanning, including:
- SSL scan
- Malware scan
- Spam scan
- SQL injection scan
- Cross-site scripting scans
- SiteLock Risk Score
Daily Code & Database Scanning and Patching, including:
- Codebase, database, and CMS scanning
- Vulnerability detection and automatic patching
Content Delivery Network (CDN) and Web Application Firewall (WAF), including:
- Malicious bot blocking
- Backdoor protection
- DDoS protection
SiteLock Business
For business and e-commerce websites
$34.99 €32.04 £27.62 AED 128.41 A$52.34 R$172.13 CA$46.78 CHF 29.86 DKK 238.96 IDR 543,622.08 ₹2,909.48 ¥5,080 MX$596.14 NZ$56.27 PHP 1,944.91 PLN 139.59 SAR 131.21 SEK 359.96 SGD 46.58 TRY 1,044.12
Complete onboarding & setup with 24/7 Access to Customer Support
- 12-hour ticket response time
Unlimited Automatic Malware Removal
- Unlimited SiteLock Expert Team Removal (excludes pre-existing infections. For removal of pre-existing infections, SiteLock 911 is required)
Website Backup (up to 10GB)
- Daily backups of website files and database
Daily Site Scanning, including:
- SSL scan
- Malware scan
- Spam scan
- SQL injection scan
- Cross-site scripting scans
- SiteLock Risk Score
Daily Code & Database Scanning and Patching, including:
- Codebase, database, and CMS scanning
- Vulnerability detection and automatic patching
Content Delivery Network (CDN) and Web Application Firewall (WAF), including:
- Malicious bot blocking
- Backdoor protection
- DDoS protection
CDN and WAF Power User and e-Commerce Controls:
- 2-factor authentication for protected/login areas via email or SMS
- Firewall PCI reporting
- Custom WAF rules editing dashboard
How SiteLock Works
We provide daily website scans to find threats, real-time notifications, automated malware removal, vulnerability/CMS patching to fix threats, a web application firewall to block and prevent harmful traffic before it ever reaches your site, a content delivery network (CDN) to accelerate your site speed (which can improve SEO) and a firewall PCI report to help eCommerce sites comply with banking institutions.
Malware Removal
Malware Detection — using our proprietary inside-out scan, we locate malware files and injected malware on your website.
Malware Removal — our technology will not only remove malware or suspicious items found on your site but it will also eliminate those uncovered in the publicly visible source code.
Website Restore — once removed, we sync the changes back to the website environment keeping you notified at every step along the way!
Content Distribution Network (CDN)
Increased speed — our network of 44+ global data centers help load your web pages up to 50% faster than sites that don’t use a CDN.
Fully secure — our CDN fully secures end-to-end encryption for any SSL certificates ensuring the highest level of security protection for your customers.
Improve SEO — a high performing CDN will boost your performance in search rankings with all the major browsers.
Web Application Firewall (WAF)
Advanced Protection — blocks attacks seeking to exploit the ten most malicious cyber threats (OWASP Top 10).
Blocks Backdoor Access — identifies backdoor files and blocks an attacker’s access.
Bad Bot Prevention — separates legitimate website visitors from automated malicious visitors.
Website Backup
Simple Site Backup — schedule automated backups or run on demand backups of all site files, folders, and databases.
Custom Restore — choose the backup version to restore or download your backed-up files in one click.
Secure Storage — data is encrypted in transit and stored in a secure SOC2 & HIPAA compliant data environment.
Trusted by Leading Brands Globally
Securing some of the world’s largest and best-known brands.
FAQs
Have another question?
Reach us by chat in the lower-right corner.
I have a small business. Can you still help?
Yes! SiteLock has website security protection and cybersecurity built for every business. While large enterprises have unlimited budgets to deal with cyberattacks, SMBs, the targets of almost half of attacks, lack the resources to defend themselves. That’s where SiteLock comes into focus. We provide affordable, powerful cybersecurity software solutions that allow small to midsize businesses to operate without fear of an attack.
Why do I need website security?
43% of all cybersecurity incidents involve small and mid-size businesses. With SiteLock, you can protect your business and customers with automated cybersecurity software solutions.
How can SiteLock help secure my online business?
SiteLock has award-winning website security solutions. With accolades from Fortress, Infor Security, and Cybersecurity our suite of website security solutions are proven and tested to provide the highest level of security for your website. This includes automated malware detection and removal, patching of CMS vulnerabilities, patching of e-commerce vulnerabilities, blocking of bad traffic, and much more.
Do your services work with all hosting providers?
Yes, our services work with all website hosting providers.
How can I help prevent malware in the future?
Update your CMS (WordPress, Joomla, Drupal, etc.), themes and plugins on a regular basis. Outdated themes, plugins and CMS are one of the main reasons websites are hacked.
Clean your hosting account regularly to decrease the risk of vulnerabilities and exploits. You can clean your account by removing all old code, unused user and FTP accounts, and unused files and domains.
Never leave a backup of your website on the same server.
Frequently update your password to combine uppercase and lowercase letters, numbers and symbols.
if you have any additional questions or concerns, please contact our Support team at (877) 563 — 2832.
I have an SSL Certificate, so why do I need this?
An SSL certificate is a great first step to a secure website and is required by search engines like Google. It decodes information passed between your site and its visitors to help prevent data theft. However, you still need to protect your site from defacement, theft of resources, and other attacks.
Still Have Questions?
Our team of experts are ready to assist you in selecting the right certificate for you.
Simply chat with us now or reach us at sales@sectigo.com or by phone: